
EKS lets the pod bring its own ECR identity. The node still decides.
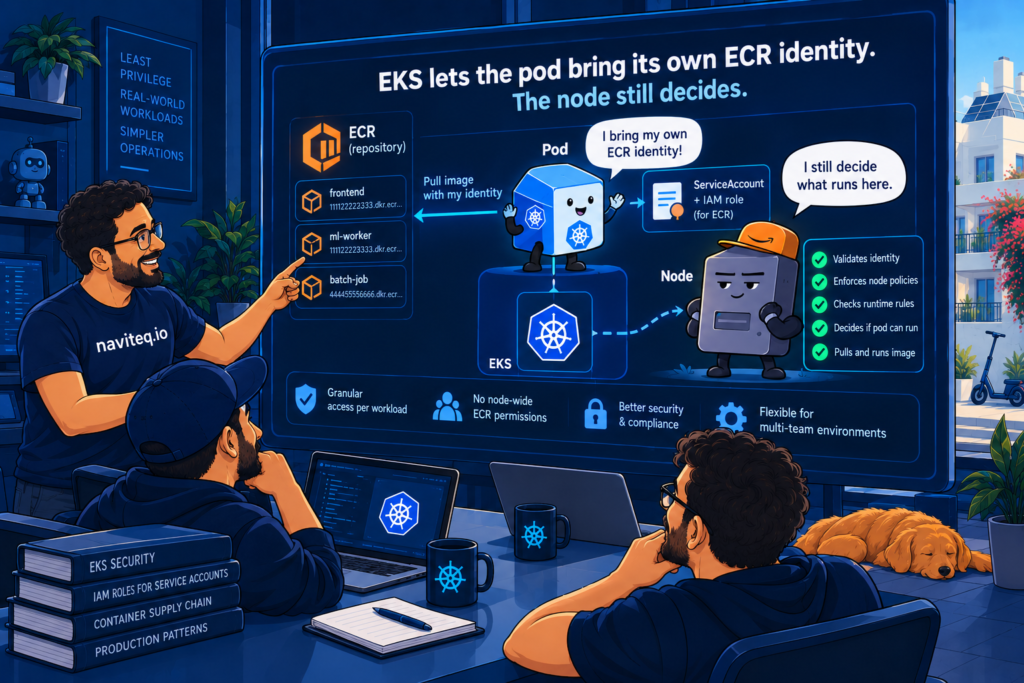
Since EKS 1.35, a pod can pull from ECR with its own IAM role instead of the node’s. Rolling it out means choosing between a fallback that leaves isolation optional and a deny that breaks every workload nobody annotated, and images already on the node are part of that choice.
Pod Certificates are GA, and the signer is now on your startup path
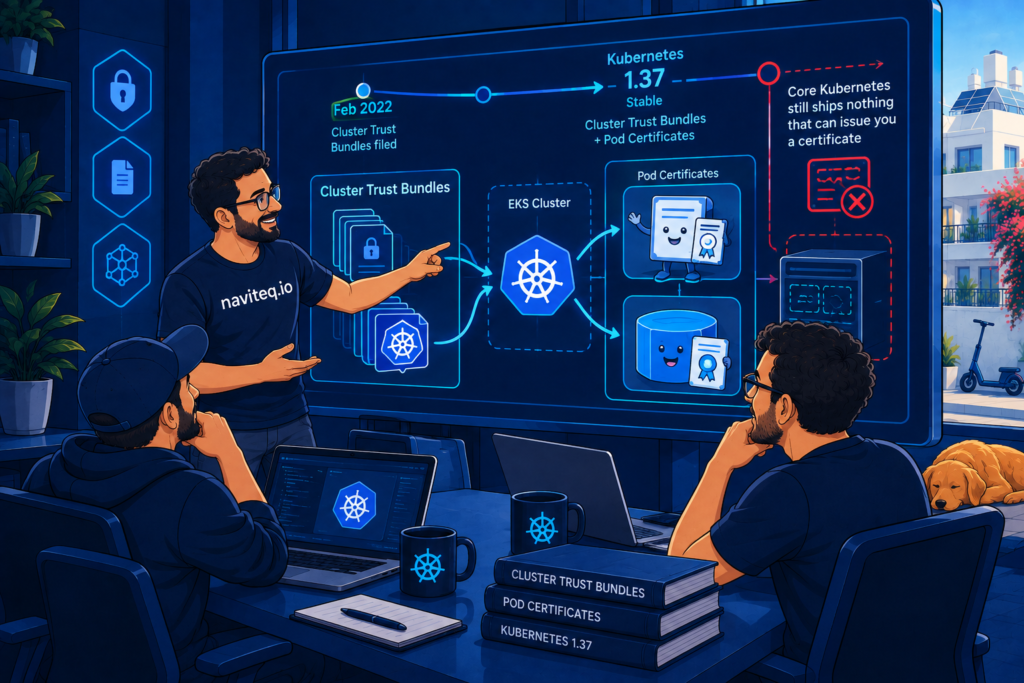
Kubernetes 1.37 made Pod Certificates and Cluster Trust Bundles stable, but core ships no signer, and the one you install decides whether your pods start at all.